Contents
Whenever I checked comments on my WordPress blog, I found more advertisements unrelated to the article. Even my article on strengthening administrator login security (in Korean) repeatedly received promotional links for debt services, furniture, projectors, and car repairs. I was opening the comment queue to read questions and feedback, only to have to sort through ads first.
Manual comment approval was already enabled. It prevented immediate publication, but the moderation queue kept growing. This time, I installed Antispam Bee to filter new comments and separately cleaned up 40 existing spam comments. Here I record the settings I applied and the results I verified on October 26, 2026.
Why spam kept accumulating with manual approval enabled
WordPress manual approval prevents comments from appearing immediately. Requests can still be received and placed in the moderation queue, however. More spam means a longer list for the administrator to review. The official WordPress comment moderation guide explains the settings for holding and publishing comments.
At the time of the check, manual approval was enabled on my blog, while Akismet was installed but inactive. I wanted to keep accepting normal comments while reducing the workload, so I decided to add a tool that sends suspicious comments to the spam folder.
Why I chose Antispam Bee
Antispam Bee checks WordPress comments, pingbacks, and trackbacks for spam. It is free for both personal and commercial sites and does not require visitors to solve CAPTCHAs. I liked being able to start without substantially adding to the steps normal visitors take to leave a comment.
It checks signals such as a hidden input field, spam patterns, and information from comments already marked as spam. For example, a bot filling in a hidden field that a normal visitor does not need to complete can provide grounds for a spam decision. The official settings documentation explains the features and options.
Installing the plugin and opening its settings
The version I installed was Antispam Bee 2.11.13, activated from the official WordPress plugin repository. To install it through the administration screen yourself, follow these steps.
- Search for Antispam Bee under Plugins → Add New Plugin.
- Check that the author is pluginkollektiv, then install and activate it.
- Open Settings → Antispam Bee and review the filtering and retention options.
- Save the settings and check the comment form while logged out too.
The plugin settings appeared in English in my administration screen. The actual screen and a summary of my selected values are included below. Labels can differ by plugin version and translation availability.
The Antispam Bee settings I applied to my blog
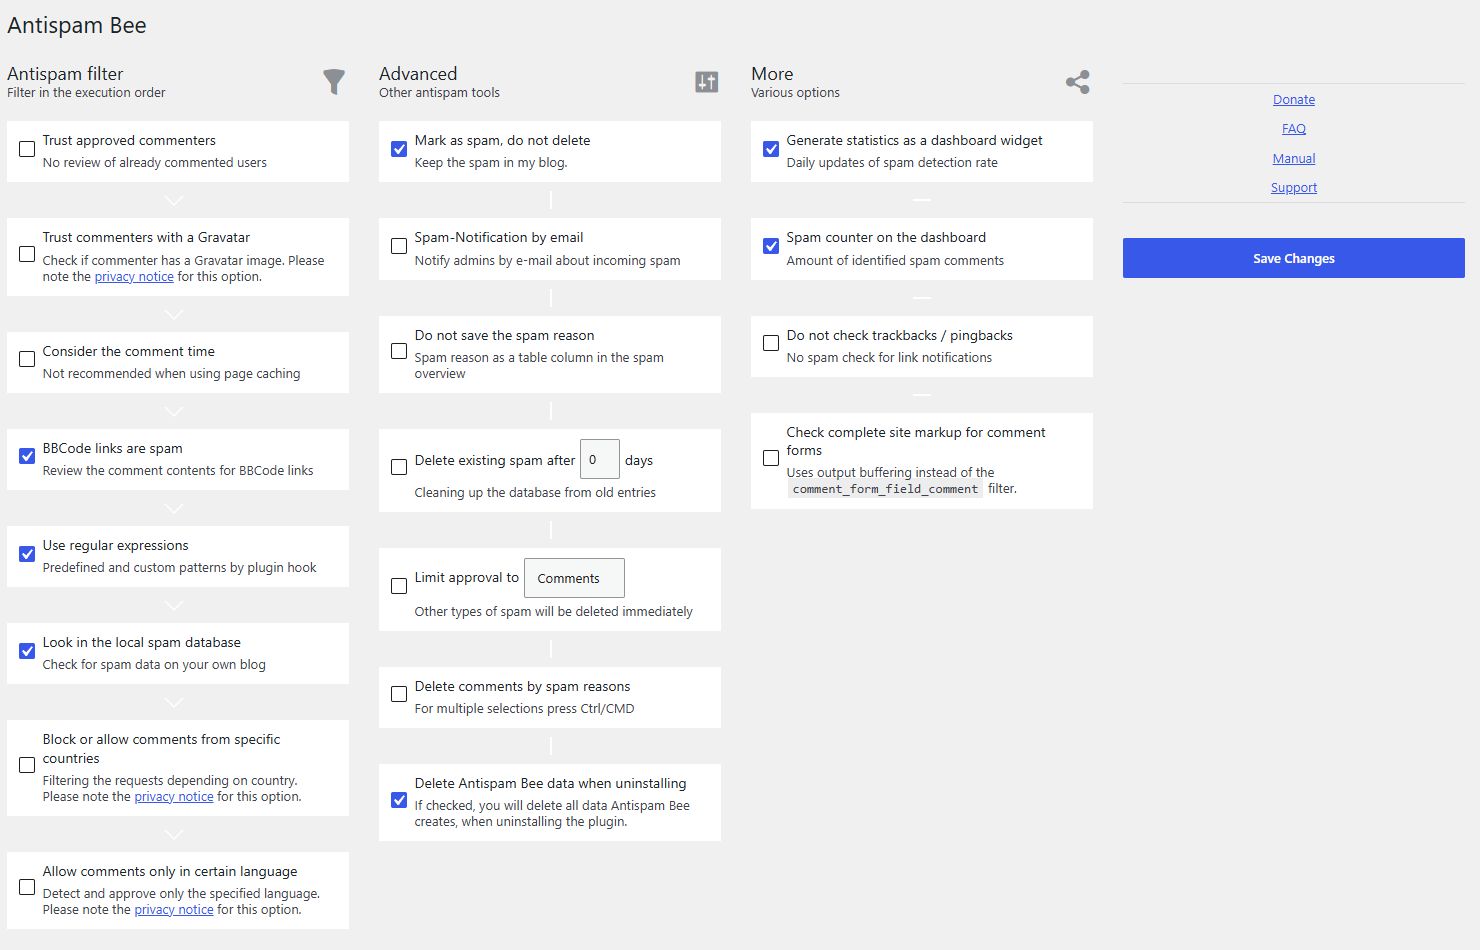
I started with settings that let me inspect and reverse automatic spam decisions rather than delete comments aggressively. I kept the existing WordPress manual approval requirement.
| Setting | Applied value | Reason for my choice |
|---|---|---|
| Manual approval for normal comments | Kept enabled | Review comments before publication even if they pass the filter |
| Mark and retain spam | Enabled | Keep comments recoverable in case of false positives |
| Save and display spam reasons | Enabled | See which check flagged a comment |
| Check local spam records and standard patterns | Enabled | Check repeated sources and known patterns |
| Check BBCode links | Enabled | Check forum-style links that my comment form does not use |
| Skip checks for approved commenters or Gravatar users | Disabled | Do not exempt comments from inspection based only on these conditions |
| Country and language restrictions | Disabled | Allow overseas visitors and English comments |
| Comment-time check | Disabled | Account for the current page-caching setup |
| Immediate deletion and age-based automatic deletion | Disabled | Inspect the initial filtering results myself |
| Email notification for each spam comment | Disabled | Use the administration spam folder instead of individual alerts |
| Dashboard statistics and counter | Enabled | Review incoming comments and filtering activity over time |
I enabled Mark as spam, do not delete. Conversely, I left the option that disables saving spam reasons unchecked, so reasons would be retained. For settings phrased negatively, check both the checkbox state and the resulting behavior.
Why I disabled the comment-time check and country/language restrictions
W3 Total Cache is active on my blog. The Antispam Bee screen also says that Consider the comment time is not recommended with page caching. I therefore left that check disabled and started with the hidden-field, local-record, and pattern checks.
I publish in Korean and English, so I did not enable country or language restrictions. Visitors may leave legitimate questions or feedback about the mods in other languages. I decided to assess spam using relevance to the article, repeated advertising text, and promotional links together.
Testing normal comments and a bot-style submission
Rather than stop at the installation notice, I read the fields in the actual public comment forms and tested the HTTP submission route without login cookies. I submitted one normal Korean comment, one normal English comment, and one bot-style comment that filled in the hidden field.
| Test | Verified saved status | What I checked |
|---|---|---|
| One normal Korean comment | Awaiting moderation | Kept the normal review process instead of sending it to spam |
| One normal English comment | Awaiting moderation | The English comment was accepted normally too |
| One bot-style submission with the hidden field filled | Spam | Confirmed the reason Honeypot in the administration list |
After identifying the three test comments by their markers, I moved them to Trash. I did not leave the bot-style test in the spam folder either. The initial statistics also include this one bot-detection test, so I did not treat that count as real-world spam-blocking performance.
Checking my separate popup comment form
Some of my mod release pages have a popup comment form in addition to the standard form. The popup clones the form at the bottom of the page, and I verified that it also copied the hidden protection field added by the plugin. While logged out, I checked that the popup opened and retained the original submission route and field names.
The successful submission checks covered the form structure and logged-out HTTP requests. I left the complete browser flow from clicking the popup submit button through to saving a comment as a further check. The official FAQ also distinguishes standard WordPress comments from custom or AJAX forms, so sites with a separate comment interface should check their submission method. Official compatibility guidance
Cleaning up 40 existing pending spam comments
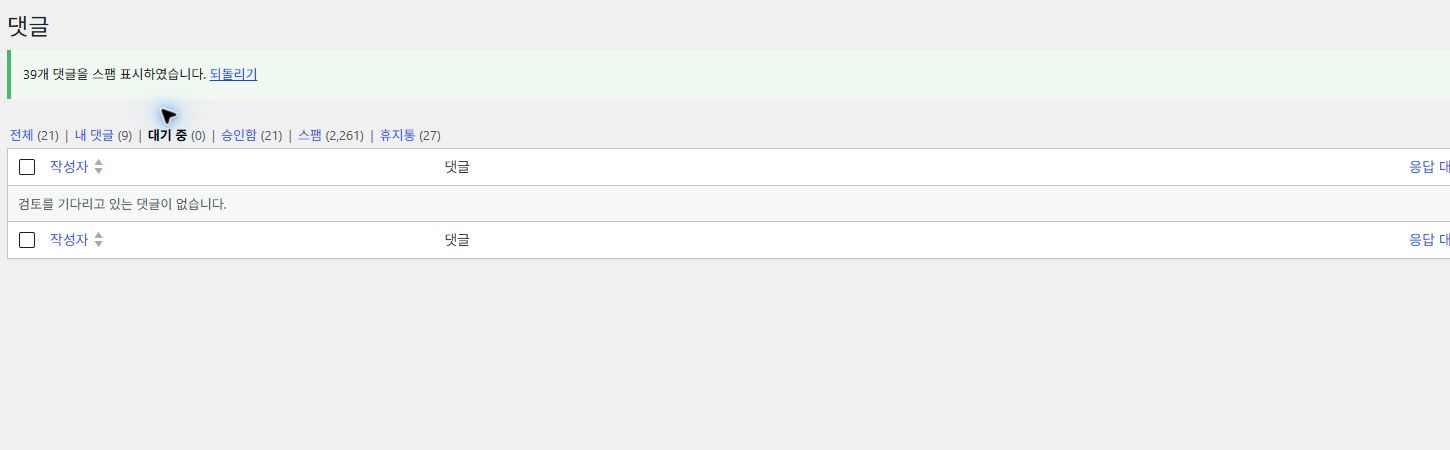
After applying the plugin, I reviewed the existing queue too. The 40 pending comments advertised debt services, furniture, projectors, and car repairs unrelated to the login-security article. After checking repeated wording and promotional links, I moved the 40 existing comments to spam myself.
| Setting | Cleanup result |
|---|---|
| Pending comments moved to spam | 40 |
| Pending comments immediately after cleanup | 0 comments |
| Previously approved comments | All 21 retained |
| Existing comments deleted | 0 comments |
These figures record my review and cleanup of the queue that existed before installation. They do not show Antispam Bee automatically rescanning and processing 40 old comments. I distinguish the new-comment filtering tests above from the existing-comment cleanup recorded in this table.
Check the spam folder for false positives after installation
I plan to check Comments → Spam alongside the normal moderation queue. If a legitimate comment is caught, I can mark it as “Not Spam,” review the reason, and adjust the settings. Until I have checked enough results, I will leave immediate and age-based automatic deletion disabled.
For this setup, I added automatic filtering to manual approval while keeping comments open and avoiding a registration requirement. I verified acceptance of normal Korean and English comments and spam classification of a bot-style submission. The long-term reduction in spam needs to be judged from future incoming comments. If missed spam or false positives appear, I will use those cases to refine the settings.
References and image credits
- Antispam Bee official plugin page — distribution, permitted uses, and compatibility.
- Antispam Bee official documentation — filtering, retention, reasons, and statistics.
- WordPress official comment moderation guide — manual approval and moderation settings.
Settings, work, and sources checked on October 26, 2026. The images are my own captures of my blog administration screens. Settings, test results, and cleanup figures are based on the records from that work. I did not use list captures exposing commenters’ email addresses, IP addresses, or individual promotional links. Screens and behavior may change with plugin versions and settings.